Security
APK file scam on WhatsApp: what one tap does to your phone
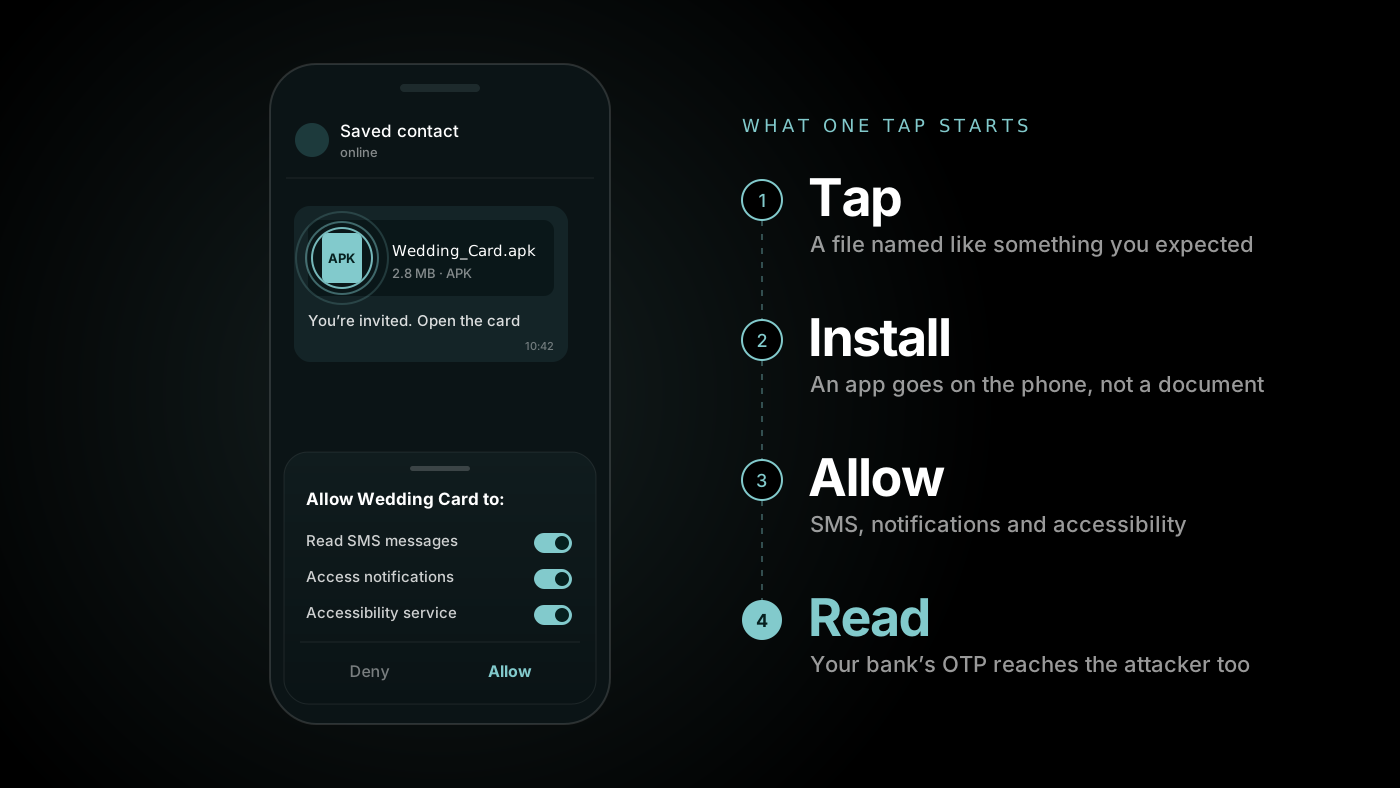
The message comes from someone you know. Attached is a file named like something you were half expecting: a wedding invitation, an electricity bill, a courier update, a KYC form. It ends in .apk, not .pdf. You tap it because the name looks right and the sender is real.
That’s the APK file scam. An APK is an Android app installer, not a document. Tapping one installs software, and once you grant what it asks for, that software can read your SMS, including the one-time passwords your bank sends. The defence isn’t a product you can buy. It’s one rule: apps come from the Play Store, never from a chat.
The uncomfortable part is that nothing technical has to fail. No zero-day, no unpatched server. Android 13 and later even block a sideloaded app from switching on accessibility or notification access until you open its settings and tap Allow restricted settings, and Google’s own help page says not to unless you trust the developer. The attack gets past that barrier the same way it got past the file name. It persuades the person holding the phone. Your firewall and antivirus are never part of the conversation.
What is an APK file, and is one on WhatsApp dangerous?
An APK file isn’t dangerous by itself. It’s the installer format for Android apps, short for Android Package Kit, and the phone’s equivalent of a .exe on Windows. The danger is where it came from. One that arrives in a chat never went through the Play Store’s review, so it installs whatever the sender built. A PDF opens and shows you something. An APK installs something, and that something asks for permissions.
What the app does once it’s installed
The permissions it asks for give the plan away: SMS, notifications, contacts, accessibility. With SMS access it reads your OTPs as they arrive, so the OTP stops being a second factor. It becomes a message the attacker gets at the same moment you do. Accessibility access goes further and lets the app see your screen and tap on your behalf.
Security researchers at CYFIRMA took apart Android malware posing as Indian bank apps in a July 2025 analysis. The samples asked for permission to read and receive SMS, and hid themselves from the app list by never registering a launcher icon.
The phone looks normal. Nothing new appears in the app drawer.
The next victim is usually in your contact list. A compromised phone is a trusted sender, so the same file goes out again from a number people recognise. That is how it reached a 46-year-old woman in Shela, Ahmedabad, who lost ₹2.62 lakh this month to a wedding invitation sent from an acquaintance’s WhatsApp.
How common is APK fraud in India?
Karnataka has the clearest numbers. Deccan Herald reported in May 2026 that the state recorded 325 APK fraud cases in 2024 and 944 in 2025, a rise of about 190 percent in a single year. Another 458 complaints came in between January and April 2026. If that pace holds, 2026 ends somewhere near 1,370. Senior citizens and retirees are among the worst hit.
Gujarat shows the supply side. In June 2026, Ahmedabad’s Cyber Crime Branch arrested three men from a Jharkhand-based network, including the alleged developer of the files, who was picked up from a moving train near Kishanganj. The complaint that started the case was a man who lost ₹6.68 lakh after one download. IANS reported that the files impersonated at least 18 banks, SBI and Axis Bank among them, along with RTO and electricity services. Twelve complaints on the national cybercrime portal and five FIRs link the gang to nearly ₹70 lakh.
One detail from that case matters more than the totals. The templates were sold through Telegram bots, on a subscription of ₹12,000 a month. You aren’t up against one clever gang. You’re up against a kit that anyone can rent.
Common APK scam messages: wedding invites, RTO challans, KYC
The name changes with whatever people are expecting that month. The mechanism doesn’t. Every lure below has turned up in the reports above.
| The file claims to be | Where it was reported | What the real one looks like |
|---|---|---|
| Wedding invitation | Karnataka, and the Shela case in Ahmedabad | A PDF, an image or a web link |
| Electricity bill notice | Karnataka, and the Ahmedabad kit | A bill on your provider’s website or its Play Store app |
| Courier or parcel alert | Karnataka | A tracking link on the courier’s own site |
| KYC update or bank reward | Karnataka, and the Ahmedabad kit (“SBI KYC”, “SBI Reward”) | Your bank’s official app, or the branch |
| RTO traffic challan | The Ahmedabad kit | The government e-challan portal |
Why is this a business problem and not just a personal one?
It’s easy to file this under personal bad luck. It stops being personal when the phone belongs to someone in accounts. Whoever approves payments is the obvious target, and the compromise happens on a device your IT policy probably says nothing about.
Your brand can be the lure, too. The Ahmedabad kit came with ready-made templates for banks, RTO notices and electricity bills. If you send customers invoices, delivery updates or account alerts, a fake of yours is one template away. The customer who gets burned remembers your name, not the attacker’s.
And your staff sit in other people’s contact lists. When a client’s phone is taken over, the file goes out to everyone in it, from a number your team has every reason to trust.
What should you tell your team?
- Apps come from the Play Store or the App Store. Never from a link in WhatsApp, SMS or Telegram, whoever sent it.
- Check the extension before tapping. An invitation is a .pdf, a .jpg or a web link. It’s never a .apk.
- If someone you know sends a file you didn’t ask for, call them. Their account may already be the one sending it.
- Treat urgency as the warning sign. Countdown timers, blocked accounts, pending fines and expiring KYC are there to stop you thinking.
- If an app you just installed tells you to find Allow restricted settings, stop there. Android put that barrier in front of exactly this kind of app.
Clicked or installed an APK file? What to do now
Tapping an APK only opens the installer. If you backed out at that screen, delete the file and you’re fine. If it got installed, speed matters more than diagnosis. In this order:
- Turn off Wi-Fi and mobile data. That cuts the app off from whoever is controlling it.
- Open Settings, then Apps, then the full app list, and sort by recently installed. Menu names vary by phone. Look for generic names like Update, System Service or Media Manager, or an entry with no name at all.
- Force stop it, then uninstall. If Uninstall is greyed out, revoke its device administrator rights first.
- Switch off any accessibility service or notification access you don’t recognise.
- Call your bank and freeze the account. Don’t wait to find out whether money has moved.
- Report it on cybercrime.gov.in or call the national cyber helpline on 1930. The sooner it’s reported, the better the chance of stopping the money before it moves on.
- Run a Play Protect scan. If anything comes back after a restart, factory reset the phone.
What this doesn’t cover
Everything above is about APK files, which are an Android mechanism, and the removal steps are Android steps. The habit at the end works on any phone. The file extension doesn’t.
Why you can’t patch your way out of this
No firewall, antivirus subscription or endpoint tool stops a person from tapping Install and then Allow. The defence is a habit. Habits come from telling people the exact thing to look for, not from telling them to be careful.
So give your team one sentence and repeat it until it’s boring: apps come from the Play Store, never from a chat.
If you’d like us to check how easily your own customer messages could be copied, or walk your team through this in a short session, tell us what you need.
Sources
- Deccan Herald, “APK fraud surges 190% in Karnataka, senior citizens among worst hit”, May 2026.
- IANS via Social News XYZ, “Gujarat Police bust Jamtara gang-linked APK fraud network, accused arrested”, 25 June 2026.
- Gujarat Samachar, “Ahmedabad Cyber Crime busts Jamtara APK fraud gang, mastermind arrested from moving train”, 25 June 2026.
- Gujarat Samachar, “Ahmedabad woman loses ₹2.62 lakh after opening fake wedding invitation APK”, 25 September 2026.
- CYFIRMA, “Android malware posing as Indian bank apps”, 25 July 2025.
- Google, Android Help, “Learn about restricted settings”.
- Indian Cyber Crime Coordination Centre, National Cyber Crime Reporting Portal, helpline 1930.